What is Skydock? A Comprehensive Solution for Idira by Palo Alto Networks (formerly CyberArk) Object Migration
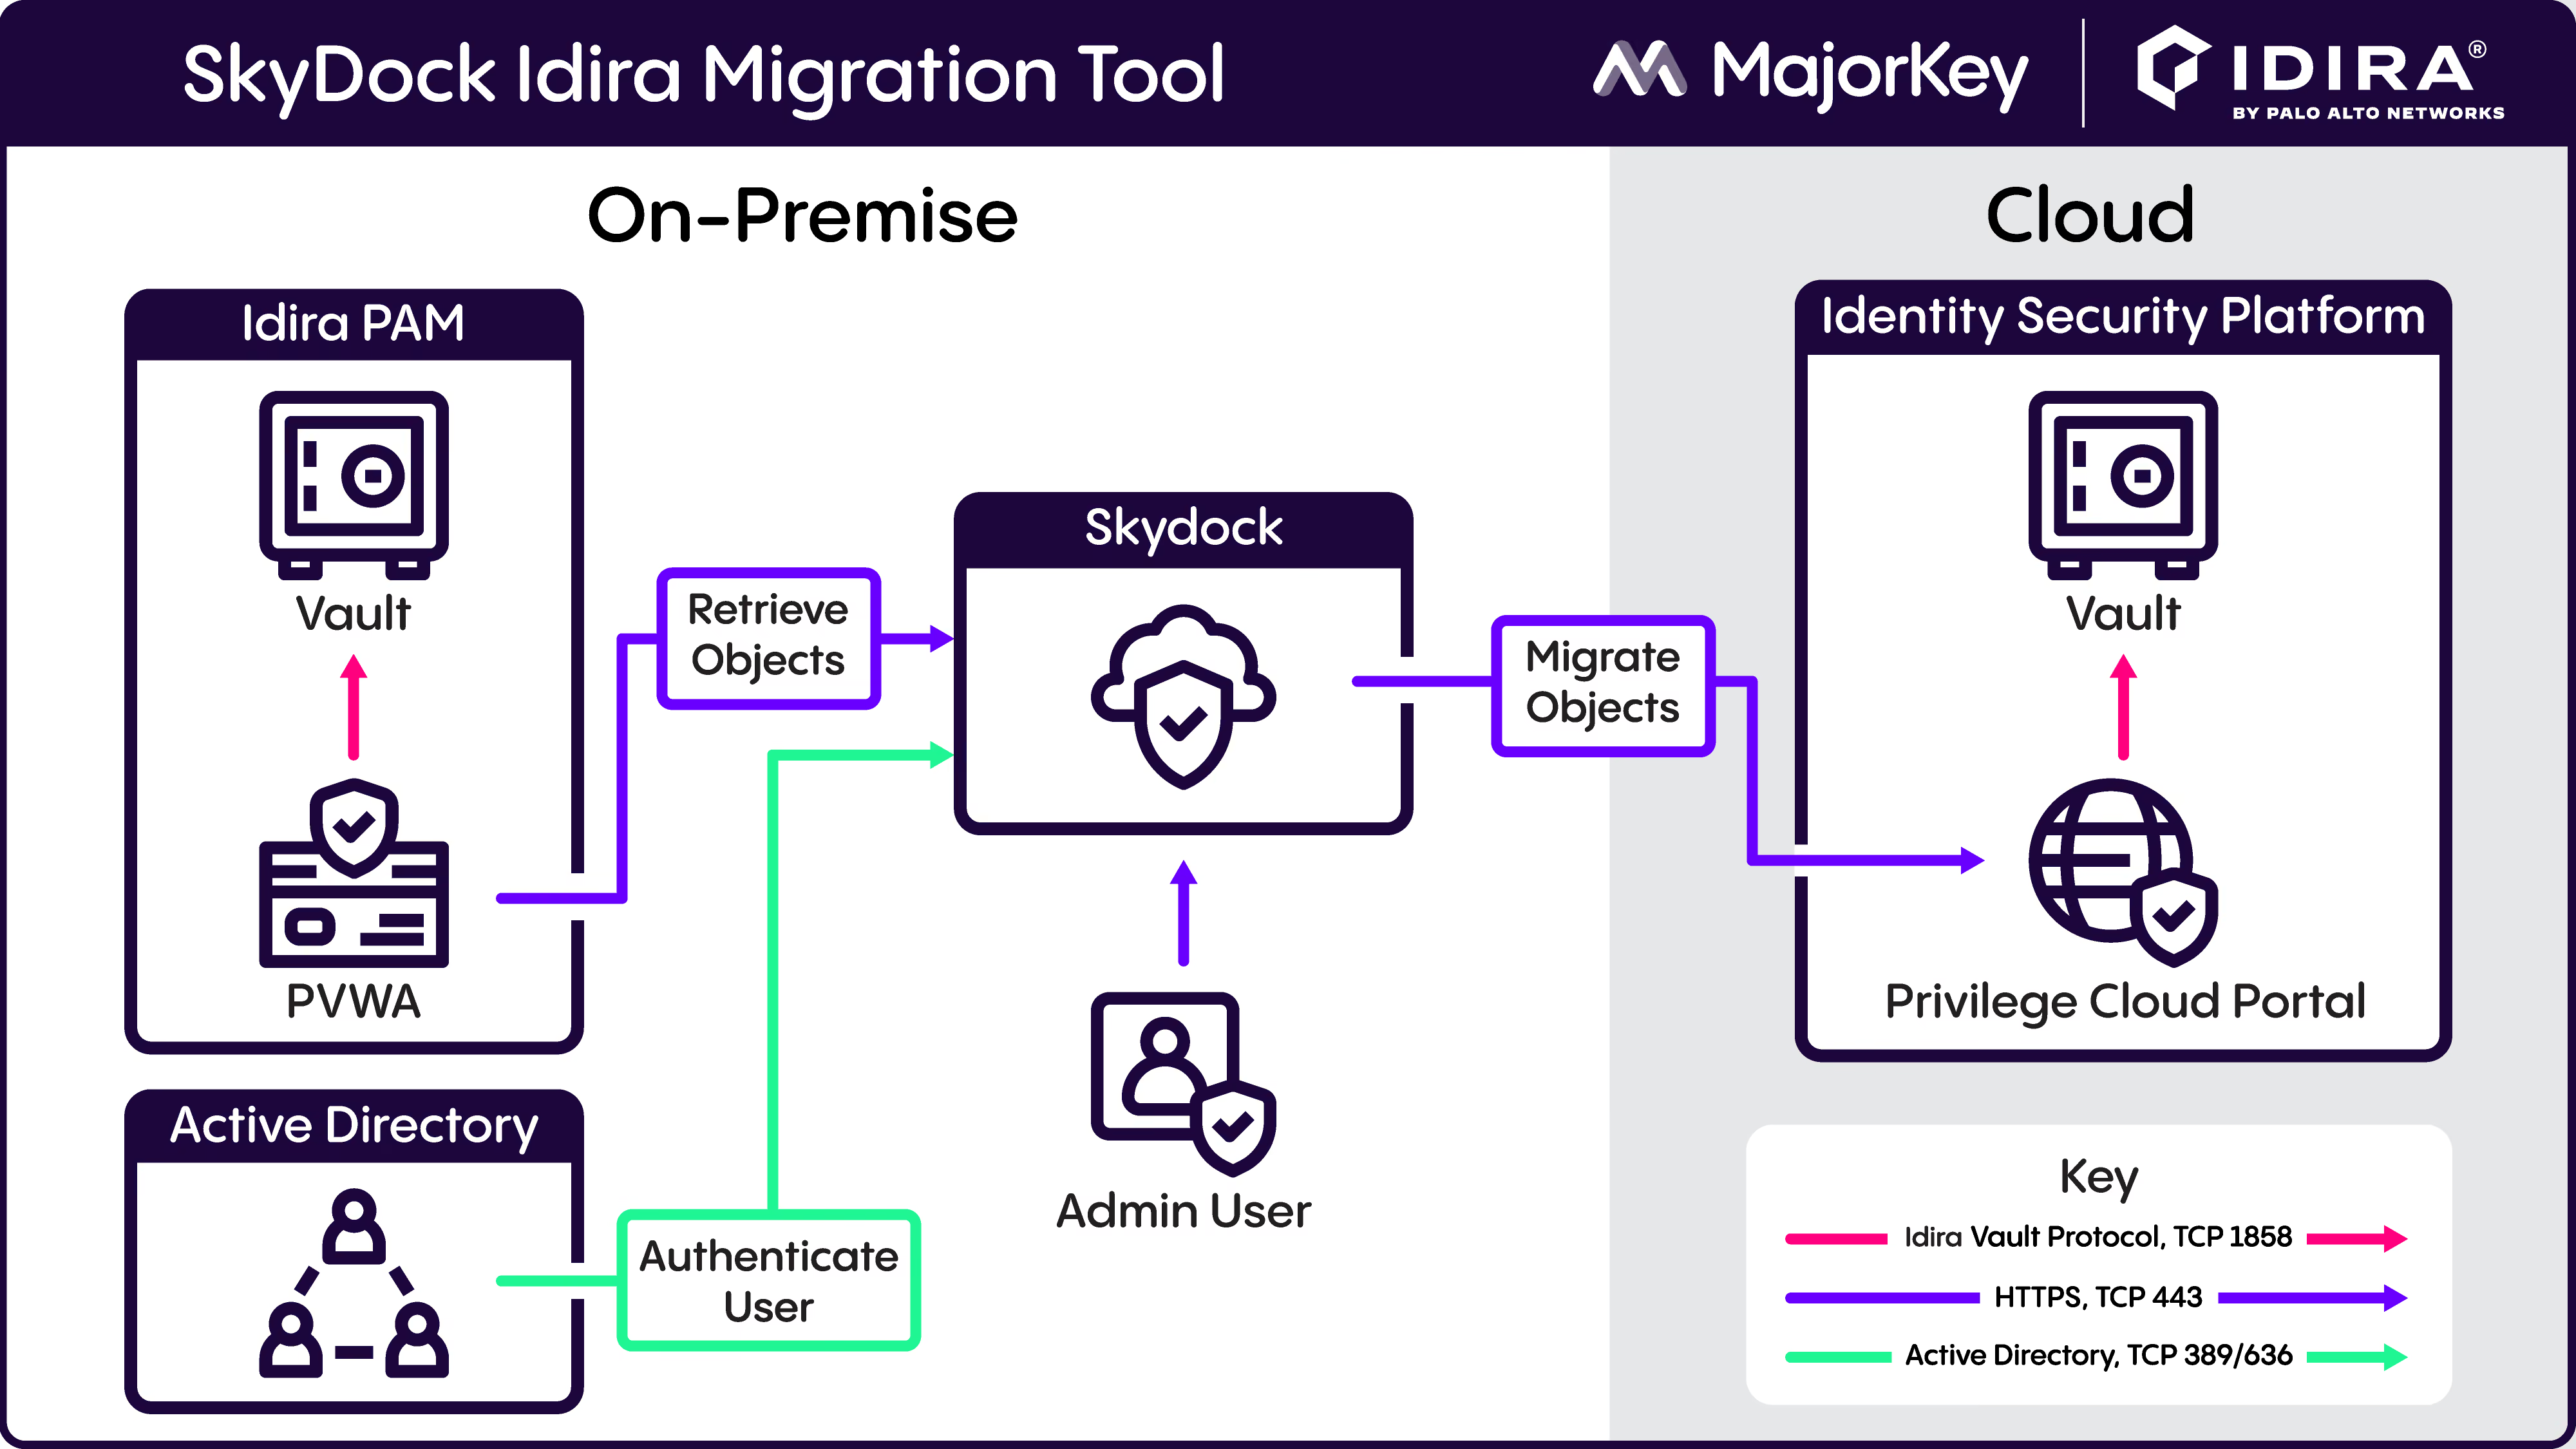
SkyDock is a robust ASP.Net Core solution designed to facilitate the seamless migration of Idira (formerly CyberArk) objects between different instances, including from on-premises installations to Privilege Cloud. With key features like Safe Member mapping, event log data collection using Idira's Export Vault Data Utility (EVD), threading to reduce migration time, selective object migration, and strict security protocols ensuring that secrets are never stored or persisted, SkyDock provides organizations with a reliable and secure tool for migration.
What is the purpose of Skydock?
The primary purpose of SkyDock is to automate and streamline the migration of Idira objects such as users, safes, platforms, and applications. This tool is particularly valuable for organizations looking to upgrade or reconfigure their Idira environments or transition from on-premises to Privilege Cloud. SkyDock minimizes downtime, reduces manual intervention, and ensures that all critical data and configurations are accurately transferred.
Core Features of Skydock
1) Seamless Migration Process
- Automated Object Transfer: SkyDock automates the migration of various Idira objects, including user groups, users, platforms, applications, safes, safe members, and accounts. This automation reduces the risk of errors and ensures a consistent migration process.
- Selective Object Migration: SkyDock provides the flexibility to select specific Idira objects for migration. This feature allows organizations to migrate only the necessary components, optimizing the migration process and focusing on critical assets.
- REST API Utilization: SkyDock leverages the Idira REST API to facilitate secure data transfer between source and destination environments, crucial for on-prem to cloud migrations.
- Secrets Management: A critical aspect of SkyDock is that secrets contained in accounts are never stored or persisted in SkyDock’s database. These secrets are retrieved from the source environment only at the time of migration and immediately transferred to the destination environment.This ensures that sensitive data remains secure and is not exposed or stored unnecessarily.
- Threading for Efficiency: SkyDock utilizes threading during the migration process to parallelize operations, significantly reducing the overall migration time. This is especially beneficial in large-scale migrations where time efficiency is critical.
- Validation and Error Handling: SkyDock includes built-in validation steps to ensure that all objects are correctly transferred.In case of errors, SkyDock’s robust error-handling mechanisms can retry operations, roll back partial migrations, or flag issues for manual resolution.
2) Safe Member Mapping
- Permission Consolidation and Redefinition: SkyDock’sSafe Member mapping feature allows organizations to consolidate or refine permissions during migration. For example, individual user permissions in the source environment can be mapped to roles or groups in the destination environment, streamlining access control management.
- Custom Mapping Rules: Administrators can define custom mapping rules to tailor the migration process, ensuring that the destination environment’s permission structure aligns with organizational policies and security requirements.
3) Event Log Data Collection Using EVD
- Comprehensive Data Capture: SkyDock integrates with Idira’s Export Vault Data Utility (EVD) to capture detailed event logs from the source environment. This ensures that all user activities, system events, and security incidents are documented and retained.
- Retention Policy Compliance: The collected logs are stored in a centralized repository within SkyDock, allowing organizations to comply with retention policies and maintain access to historical event data, even after migration to the cloud.
- Audit and Forensic Capabilities: The availability of comprehensive logs post-migration supports audit readiness and enhances security by providing a clear trail of all system activities.
4) Handling On-Prem to Privilege Cloud Migration
- Mapping On-Prem Features to Cloud: SkyDock includes logic to map on-prem features to their equivalents in Privilege Cloud. This ensures that all critical security and operational features are preserved, orappropriately adjusted, during the migration.
- Seamless Data Transfer: SkyDock handles the secure transfer of data and configurations, ensuring that all elements of the Idira environment are accurately and efficiently migrated to Privilege Cloud.
- Post-Migration Benefits: After the migration, organizations benefit from a well-structured and consistent environment in Privilege Cloud in-line with their previous instance.
Security and Compliance Capabilities
SkyDock is designed with security and compliance as a priority. By ensuring that secrets are never stored or persisted, by utilizing threading to enhance efficiency, by allowing selective migration of objects, and by maintaining detailed logs and audit trails, SkyDock helps organizations meet regulatory requirements and internal security standards.
In Conclusion
SkyDock is a comprehensive solution for organizations looking to migrate their Idira environments, whether upgrading on-prem installations or transitioning to Privilege Cloud. With features like Safe Member mapping, event log data collection via EVD, threading to reduce migration time, selective object migration, strict secrets management, and robust automation, SkyDock simplifies the migration process, reduces risks, and ensures that all critical security and operational needs are met.
Authors