Introducing NomadID: Mission-Ready Identity Management for Federal Agencies in DDIL Scenarios

September 23, 2025
|
Duration:
3
min READ
Introducing NomadID: Mission-Ready Identity Management for Federal Agencies in DDIL Scenarios
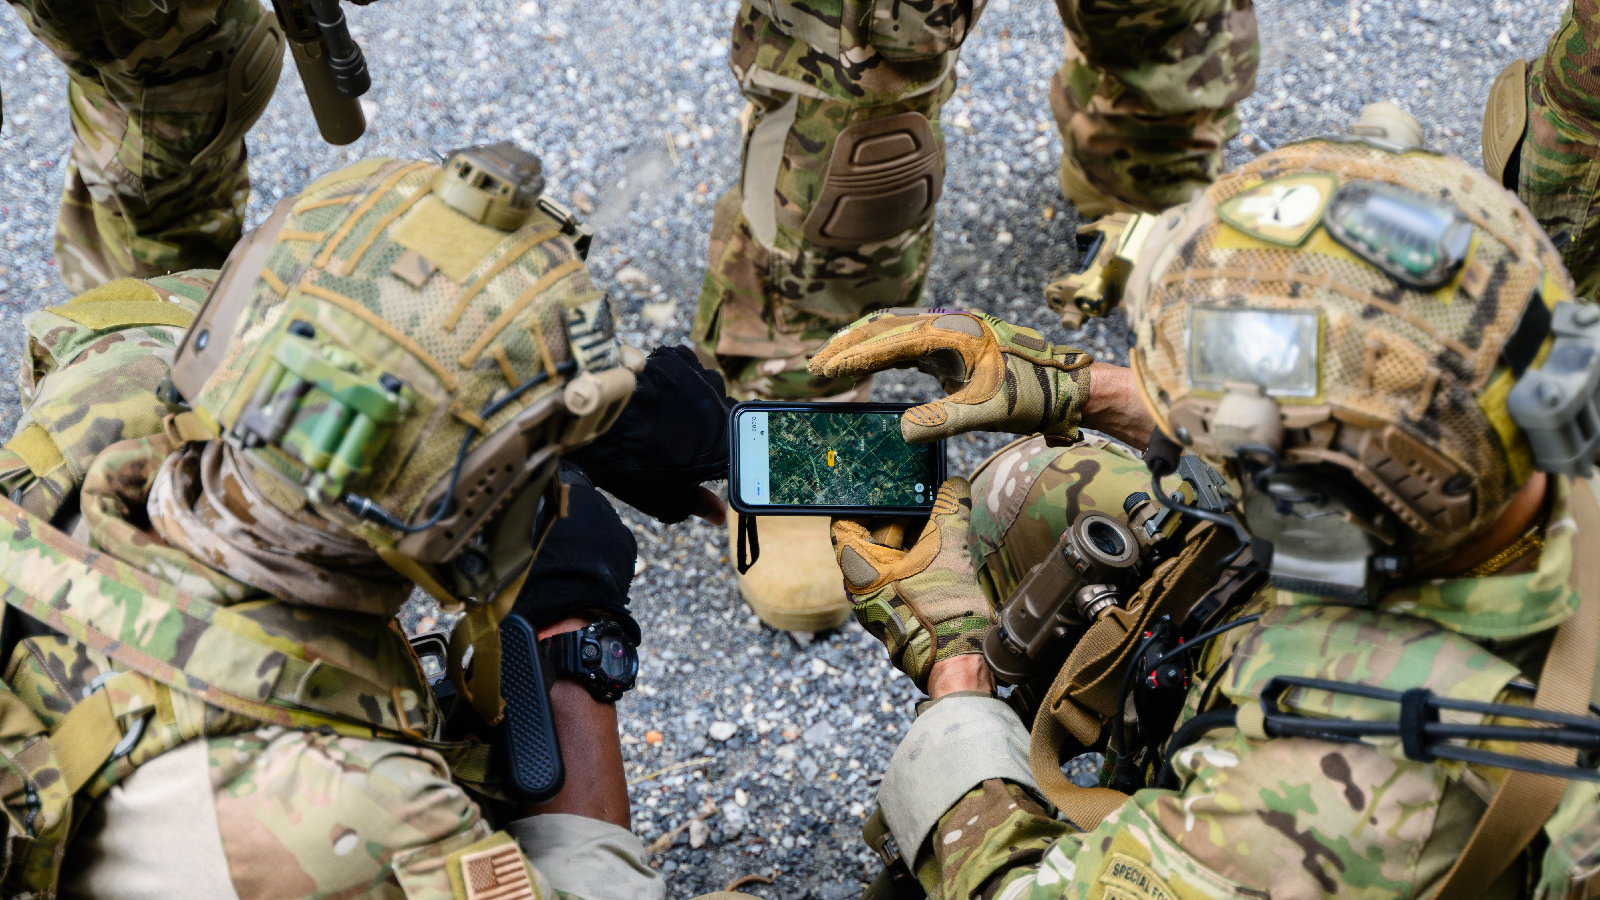
NomadID provides adaptable single sign-on and security for DOD agencies in disconnected and low-bandwidth scenarios.

Disconnected, Denied, Intermittent, Low-Bandwidth (DDIL) and air-gapped network environments are common, and sometimes required, in Department of Defense (DOD) environments. Units may deliberately choose to operate in DDIL environments, but equipment failures, outages, or hostile action can force them to operate in these environments. In either case, DOD units must retain access to critical systems to ensure mission success. This includes having a flexible and resilient Identity, Credentialing and Access Management (ICAM) solution that enables agencies to maintain uninterrupted application access during outages.

Created by Oxford Comptuter Group, a MajorKey Technologies Company, and partners, NomadID is designed to ensure uninterrupted authentication and single-sign-on (SSO) capabilities for agencies operating under challenging or disconnected conditions. It is a robust and versatile solution designed specifically to ensure the uninterrupted availability of authentication and single sign-on (SSO) capabilities for organizations operating under challenging conditions. This includes environments characterized by disconnections, intentional denials, intermittent connectivity, and/or limited bandwidth.

NomadID addresses the complexities agencies face when needing to operate efficiently under demanding conditions, providing a streamlined and reliable authentication experience. The solution helps agencies ensure security standards are met, even when faced with equipment failures, outages, or hostile action.

By focusing on this multifaceted approach, NomadID provides a seamless and reliable authentication experience that upholds security standards and user convenience – even when the network conditions are less than ideal.

The solution includes components for identity management, security monitoring, and identity governance, with a primary identity source and provisioning mechanisms for authentication and SSO for applications and services at the edge. The identity services are co-located with authentication components to provide identity management and governance in both connected and disconnected operations.

Solution Benefits

  • Uninterrupted Access and Operational Continuity: Ensures continuous authentication and SSO, even during outages or low-bandwidth conditions, minimizing downtime and keeping agencies operational and efficient.
  • Enhanced Security and Resilience: Reduces the risk of unauthorized access and protects against vulnerabilities during system failures with a robust backup mechanism that maintains secure identity management.
  • Adaptability Across Environments: Supports seamless access management in various conditions, including remote or disconnected environments, regardless of connectivity issues or geographical constraints.
  • Improved User Experience and Compliance: Provides a seamless login experience while meeting regulatory requirements and internal security policies with consistent access controls and audit trails.
  • Cost Efficiency: Reduces the negative impact of downtime by ensuring resilient identity management systems, decreasing the need for costly emergency interventions

Resources

Contact nomadid@majorkeytech.com to learn more.
‍

Authors

No items found.

Recent Blogs

Blog

How to Evaluate an Identity-First AI Advisory Partner

Learn what to look for in an AI advisory partner, from non-human identity governance and delegated authority to operational execution and measurable outcomes.

Blog

How to Accelerate Your Idira Privilege Cloud Migration Without Increasing Risk

Learn how enterprise teams evaluate, plan, and execute successful Idira cloud migrations while minimizing downtime, complexity, and operational disruption.

Blog

Preparing Your Identity Program for Agentic AI

Agentic AI extends identity governance beyond access. Learn how to govern authority, accountability, and autonomous decision-making across AI-driven operations.

Blog

Automating and Optimizing Enterprise Application Onboarding: Have You Checked Your Blind Spots?

Discover the most common application onboarding bottlenecks and blind spots, how leading organizations automate workflows, and ways to assess and improve maturity.

Blog

Is Your Organization Ready for Enterprise AI?

Learn how to govern shadow AI, AI agents, and non-human identities while establishing the visibility, ownership, and access controls required for enterprise AI adoption.

Blog

Why Identity Must Come Before AI

AI risk often shows up first as identity risk. Learn the IAM capabilities and governance controls required to deploy and scale AI securely.

Blog

Why CISOs Are Shifting from On-Premises to Idira Privilege Cloud

Discover why enterprises are migrating from self-hosted Idira PAM to Idira Privilege Cloud to reduce operational risk, simplify maintenance, improve scalability, and support compliance initiatives.

Blog

AI Readiness Is a Security Problem: What to Fix Before You Scale Copilot

Many organizations struggle to move beyond AI pilots because they lack clarity around risk, access, ownership, and investment priorities. MosaicStack brings those decisions together in three days.

Blog

Building a Scalable IAM Application Onboarding Strategy

A scalable application onboarding strategy helps organizations move faster by treating onboarding as a repeatable business program rather than a one-time technical task.

Blog

Notes from the Field: 5 Challenges Endemic to Copilot Rollouts

Copilot and agentic AI rollouts surface the permissions, labels, access paths, and adoption gaps that already exist in your environment. How do you fix them?

Blog

Understanding LDAP Signing and LDAP Channel Binding Requirements

Active Directory Domain Services relies heavily on LDAP, but not every LDAP connection is automatically protected against interception, modification, or authentication-relay attacks.

Blog

Microsoft Entra ID Retires SMS & Voice Authentication: Why Passkeys Are the New Default

Microsoft Entra ID is sunsetting native SMS and voice MFA to make phishing-resistant passkeys the default.

Blog

Modernizing PAM for the Identity Era: Expanding Beyond Traditional Privileged Accounts

Learn why modern PAM strategies must extend beyond administrator accounts to include machine identities, cloud entitlements, Just-in-Time access, and Zero Standing Privilege. Dan Ross shares practical guidance for building a scalable privileged access program.

Blog

Make AI Boring

As AI becomes more deeply embedded across the enterprise, leaders must focus on the decisions, tradeoffs, and accountability required to scale responsibly.

Blog

Microsoft Entra ID’s SSPR Update and How to Mitigate its Operational Risks

What C-suite leaders need to know about the upcoming Microsoft Entra ID SSPR changes, its operational risks, and how to mitigate them.

Blog

Why IAM Becomes the Critical Path in Application Delivery

IAM isn't why most projects start, but it's often why they stall. Learn how proactive identity governance accelerates application delivery.

Identity Governance
Privileged Identity
Customer Identity
Workforce Identity
Deployment and Integration
Federal