Authentication vs Authorization for CIAM Tools
Within the context of Customer Identity and Access Management tools, the concepts of authentication and authorization are two fundamental concepts, both filling different requirements.
Authentication
What is Authentication in the context of CIAM?
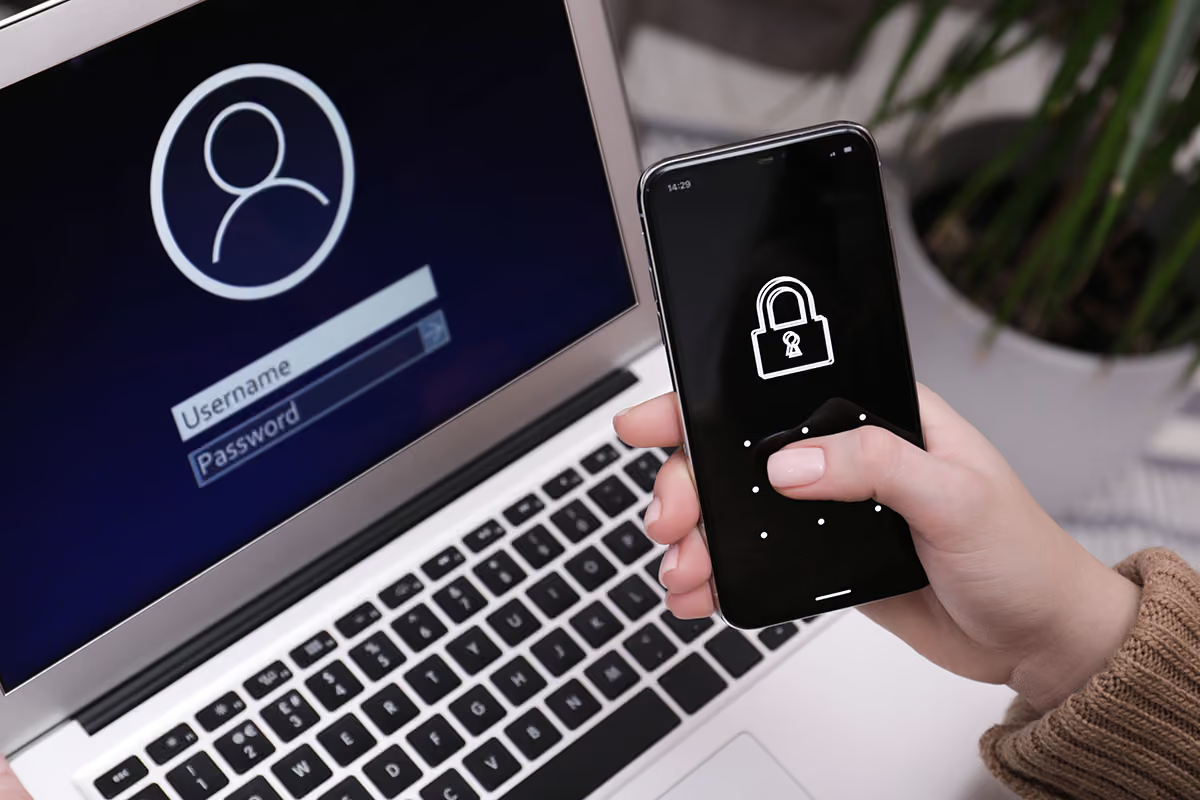
This is the process of verifying the identity of a user when attempting to gain access to an application, data, or system. This process involves verifying the user has the correct credential, which can include username and password, biometric data, or security tokens.
Authentication is most commonly the first step of the login process, allowing credential verification prior to allowing access.
What are the most common forms of user Authentication in CIAM tools?
All CIAM tools use some form of user identity authentication to verify and validate who is logging in. Some of the most common forms of authentication employed by CIAM tools include:
Username and password authentication
By far the most common form of authentication, but also one of the weakest in terms of security. This form is very vulnerable to risks such as phishing and poor password hygiene that can result in breaches.
Multi-factor authentication (MFA)
This form of authentication requires users to verify their identity through two or more methods. This can include a code generated by smartphone apps, sent by SMS, or sent via email. This is generally a stronger form of authentication than just username and password, but it also has weaknesses such as losing a phone or lack of cell service.
Biometric authentication
This process uses unique physical identifiers to authenticate a user. This form of authentication is becoming widely adopted to its high level of security while being frictionless for the end user with smartphones able to verify fingerprint or face scan.
Certificate-based authentication
Certificate-based authentication relies on digital certificates to validate the identity of a user. At a high level, a digital certificate is stored on the user’s phone or device. The certificate is then checked and validated when the user attempts to access an application or system, and if the data in the certificate is authenticated then access is allowed. The process is a little more complex than that and Ping Identity does a great job of explaining in more depth if you’re interested.
Social media authentication
This form of authentication allows users to authenticate themselves by logging into an existing social media account. By integrating with popular social platforms, users can access services without needing to create new credentials.
Passwordless authentication
One of the biggest buzzwords in the industry, password authentication seeks to remove the need for passwords. Rather than using a password, this form of authentication relies on factors like biometrics, hardware tokens or single use codes. Passwordless is one of the most secure forms of authentication.
How does Single Sign-On (SSO) and federated identity management impact authentication?
SSO and federated identity are both authentication mechanisms that help reduce friction within the authentication process. They are not a method of authentication on their own, but rather utilize these methods listed above to facilitate authentication across multiple systems/applications and organizations.
- Single Sign-On allows a user to authenticate one time for access to multiple applications with a single organization. By eliminating the need to repeatedly enter credentials, it helps create a seamless user experience.
- Federated identity takes the concept of SSO and extends it across multiple organizations. It allows a user to login into one organization and then access resources/data in another organization without having to enter credentials or have a separate account. Security protocols such as SAML or OpenID are used by organizations to support the exchange of user identity information.
Authorization
What is Authorization in the context of CIAM?
Authorization, which is also known as access control, is the process of determining the level of access a user should be allowed to access once their identity has been authenticated. The process defines the scope of permission and privilege associated with the identity and the level of access that is required.
Typically, the authorization process ensures that users are only granted required access based on their role, group membership, or other internally defined criteria. The end goal of the authorization is verifying a user has the minimum level of access to protect sensitive data and information.
What are the most common forms of user Authorization in CIAM tools?
Authorization is a key component of CIAM tools, with the three most common forms being Role-based Access Control (RBAC), Attribute-based Access Control (ABAC), and Policy-based Access Control (PBAC).
- Role-based Access Control (RBAC): RBAC is a model in which every user is assigned a pre-defined role which then dictates access privileges. This helps simplify access management by avoiding having to grant specific permissions to individual users.
- Attribute-Based Access Control (ABAC): ABAC is an authorization model that considers various attributes, such as user attributes (e.g., age, location, membership), environmental attributes (e.g., time of day, network location), and resource attributes (e.g., sensitivity, classification). Access decisions are made based on policies that evaluate the combination of attributes.
- Policy-based Access Control (PBAC): PBAC is an authorization model that is externalized to the Business and dynamic in nature. Acceptable use policy and Learning Management System policies (LMS integration) are a few examples. Access decisions are then made based on policies that evaluate the dynamically changing business model.
The availability and configuration of specific authorization methods may vary depending on the CIAM tool's capabilities and the organization's requirements. Organizations typically have flexibility in configuring and customizing the authorization model that aligns with their security policies and access control needs.
In conclusion
With the right combination of authentication and authorization, organizations can enhance user experience while bolstering security and data privacy. The right approach to authentication and authorization methods comes down to the specific business needs and requirements of an organization. If you need help determining whether you have the right approach for your organization, we’re offering a free one-day CIAM advisory engagement. We are also happy to connect you with a CIAM expert for any other questions you may have, feel free to contact us here.